A universal wave of cyber attacks and data breaches started in early January after four zero-day exploits were discovered in on-premises Microsoft Exchange Servers. Zero-day exploits are unknown exploits in the wild that exposes a vulnerability in software or hardware and can create complicated problems well before anyone realizes something is wrong. At first, a zero-day exploit leaves no opportunity for detection, giving attackers full access to user emails and passwords, administrator privileges, and access to connected devices on the same network. As of March 9, 2021, it was estimated that 250,000 servers fell victim to the attacks, including servers belonging to around 30,000 organizations in the United States.
Zero-Day Exploits
A zero-day exploit exposes a vulnerability in software or hardware. A zero-day attack happens once that software or hardware vulnerability is exploited and attackers release malware before a developer has an opportunity to create a patch to fix it. A great example would be a company’s developers creating software that contains an unknown vulnerability. An attacker notices the weakness before the developer does or even has a chance to fix it. The attacker writes and executes exploit code while the vulnerability is still available. In most cases, either the public recognizes the flaw in the form of identity theft, or the developer catches it and creates a band-aid (patch) to stop the bleeding. These types of attacks are seldom discovered immediately. Sometimes it takes months or years before a developer learns of the vulnerability that led to the attack in the first place.
What Happened with the Microsoft Server Exchange Hack?
Microsoft Exchange Server is an email inbox, calendar, and collaboration solution with users ranging from corporate giants to small and medium-sized businesses around the world. Microsoft was made aware of four zero-day bugs sometime in early January by a DEVCORE researcher. In early March, Microsoft released patches to stop the four critical exposures in its Microsoft Exchange Server software. At the time, Microsoft announced that the bugs were being actively exploited in limited, targeted attacks. It is believed that the hackers acquired Proof-of-Concept attack code that Microsoft shared with antivirus companies as part of the company’s Microsoft Active Protections Program (Mapp).
While bug fixes have been released, the extent of Exchange Server hack depends on the speed and application of the patches, meanwhile, the number of victims continues to increase. Microsoft is also looking into possible links between Proof-of-Concept attack code issued privately to cybersecurity partners and vendors before the patch release.
SolarWinds Orion: The Biggest Hack of the Year
Who is Responsible for the Cyber-Attack?
Microsoft has announced that the recent Server Exchange attacks using the zero-day flaws were traced back to Hafnium. Hafnium is an advanced persistent threat (APT) group from China. Originating in China, Hafnium uses a network of virtual private servers (VPS) located in the US to conceal their location. However, Microsoft said they have continued to see an increase in the use of these vulnerabilities in attacks targeting unpatched systems by multiple malicious groups outside Hafnium. When zero-day vulnerabilities are discovered and emergency security patches are released, the effects can be substantial. Problems can often be traced back to awareness of new patches, slow uptake, or reasons why IT staff cannot apply a fix.
Which Vulnerabilities Were Exposed?
According to Microsoft, the vulnerabilities, known as ProxyLogon, impacted on-premises Exchange Server 2013, Exchange Server 2016, and Exchange Server 2019. Microsoft’s Exchange Online was not affected.
Here is a list of the vulnerabilities that were exposed in the attack:
- CVE-2021-26855: CVSS 9.1: a Server Side Request Forgery (SSRF) vulnerability leading to crafted HTTP requests being sent by unauthenticated attackers. Servers need to be able to accept untrusted connections over port 443 for the bug to be triggered.
- CVE-2021-26857: CVSS 7.8: an insecure deserialization vulnerability in the Exchange Unified Messaging Service, allowing arbitrary code deployment under SYSTEM. However, this vulnerability needs to be combined with another or stolen credentials must be used.
- CVE-2021-26858: CVSS 7.8: a post-authentication arbitrary file write vulnerability to writes to paths.
- CVE-2021-27065: CVSS 7.8: a post-authentication arbitrary file write vulnerability to writes to paths.
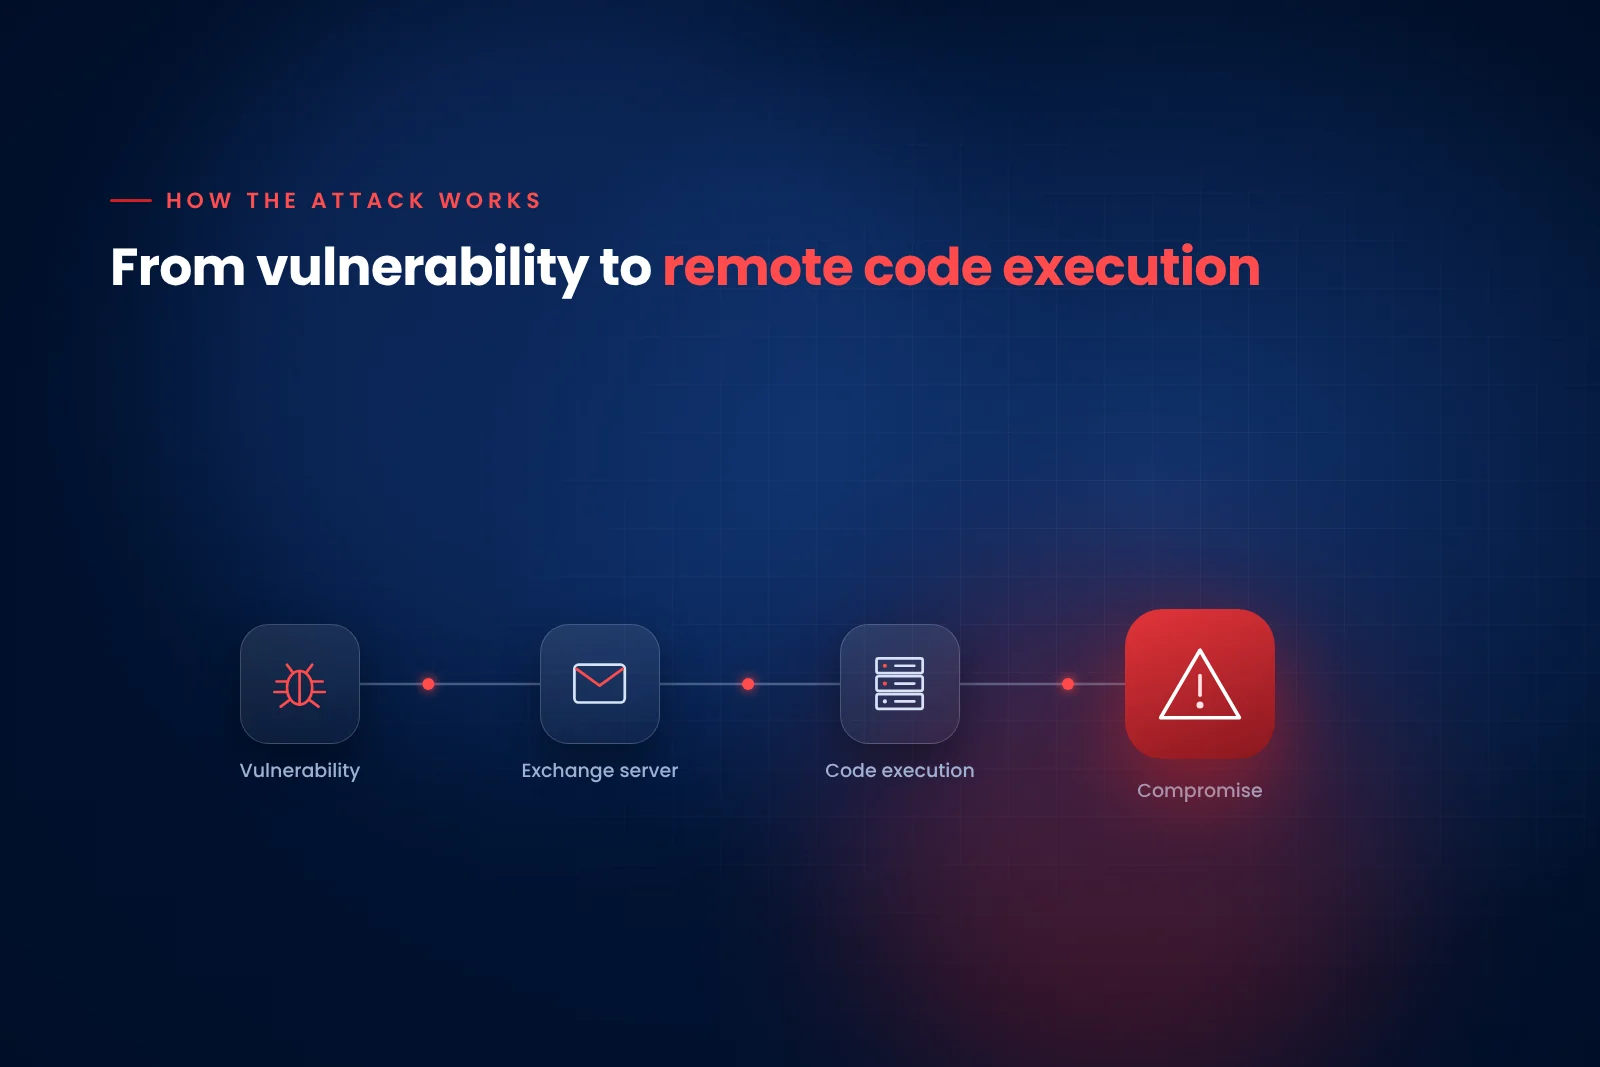
If used in an attack chain, all of these vulnerabilities can lead to Remote Code Execution (RCE), server hijacking, backdoors, data theft, and potentially further malware deployment.
How You Can Check Your Servers for Vulnerability
Microsoft is advising IT administrators and customers to apply the security patches without delay. However, just because patches are applied doesn’t mean that servers haven’t already been compromised. The tech giant has published a script on GitHub available to IT administrators to run that includes indicators of compromise linked to the four vulnerabilities. If there are any signs of suspicious behavior dating back as far as September 1, 2020, the Cybersecurity and Infrastructure Security Agency (CISA) needs agencies to disconnect them from the Internet to mitigate the risk of further damage.