Retiring healthcare IT equipment is not as simple as unplugging old devices and sending them to storage. If a laptop, server, hard drive, SSD, tape, phone, or storage array contains protected health information, your organization still has a duty to protect that data during disposal.
Under HIPAA, covered entities and business associates must use reasonable safeguards when disposing of PHI and electronic PHI. That means your disposal process should control access, remove or destroy data, document the outcome, and prove what happened to each asset.
This HIPAA disposal checklist can help your team retire used IT equipment safely, reduce compliance risk, and recover value where equipment still has resale potential.
What HIPAA Requires During Disposal
HIPAA does not require one single disposal method for every device. Instead, healthcare organizations must choose reasonable safeguards based on the risk, the data type, and the media involved.
For electronic PHI, that usually means three things:
- Create policies for final disposition of hardware and electronic media.
- Remove electronic PHI before media is reused.
- Train staff who handle equipment disposal.
The U.S. Department of Health and Human Services explains that electronic media may be cleared, purged, or destroyed depending on the situation. NIST SP 800-88 Rev. 2 also gives organizations a practical framework for media sanitization.
HIPAA Disposal Checklist
Use this checklist before selling, recycling, donating, returning, or destroying healthcare IT equipment.
1. Identify Every Device That May Contain PHI
Start with a complete inventory. Include any equipment that may store, process, or connect to patient data.
Common assets include:
- Laptops and desktops
- Servers and storage arrays
- Hard drives and SSDs
- Backup tapes and removable media
- Tablets and mobile devices
- Medical workstations
- Network appliances
- Printers, copiers, and scanners with internal storage
Do not assume a device is safe because it is old, broken, or no longer connected to the network. Retired equipment can still contain recoverable data.
2. Classify the Data Risk
Before choosing a disposal method, decide what level of risk each asset carries. A front-desk computer, imaging workstation, EHR server, and backup tape may all need different handling.
Ask these questions:
- Did the device store PHI or ePHI?
- Did it connect to an EHR, billing, lab, imaging, or pharmacy system?
- Does it contain local user profiles or cached files?
- Is the storage media functional?
- Does your policy require destruction instead of reuse?
Higher-risk assets should receive stricter controls and more detailed documentation.
3. Build a Chain of Custody
Chain of custody shows who handled each asset, when it moved, and where it went. This matters because disposal risk does not end when equipment leaves your building.
Your chain of custody should include:
- Pickup date and location
- Asset type, serial number, and tag number
- Quantity and condition
- Person or vendor receiving the equipment
- Transport method
- Processing location
- Final disposition
For bulk healthcare refreshes, use serialized reporting instead of a simple receipt. A box count is not enough for audit-ready disposal.
4. Choose the Right Data Destruction Method
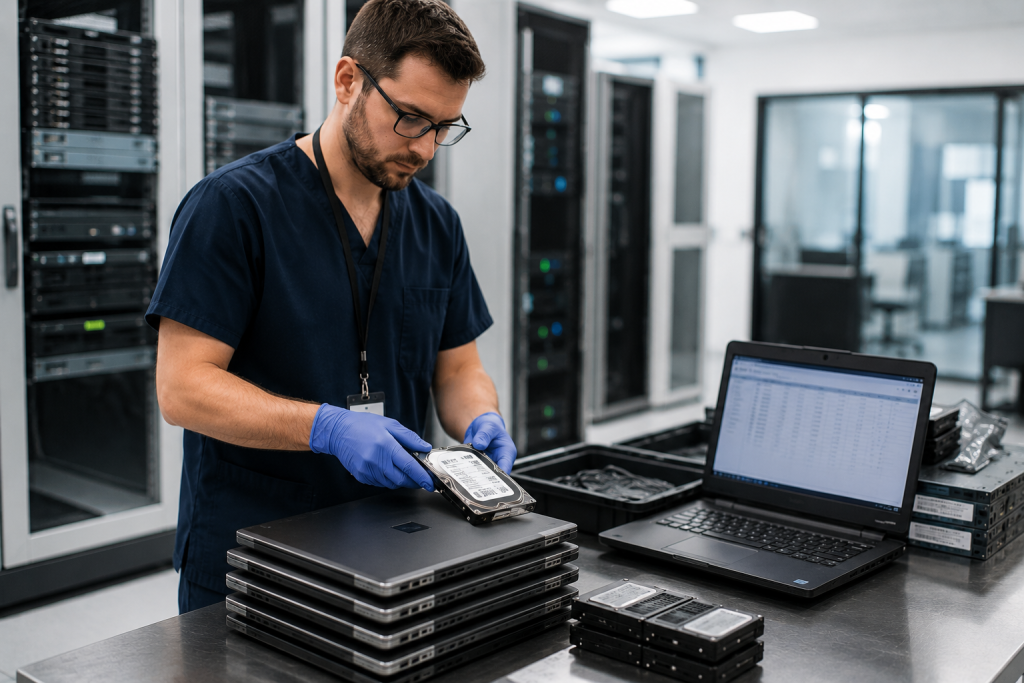
Data destruction should match the asset, media type, and risk level. Common methods include clearing, purging, degaussing, shredding, crushing, or other physical destruction.
For reusable equipment, NIST-aligned sanitization may allow the hardware to be resold after data has been removed. For failed drives, unknown media, high-risk records, or policy-driven destruction, physical destruction may be the safer option.
We Buy Used IT Equipment helps organizations retire used healthcare IT assets with secure processing, documentation, and buyback options. For equipment that can be reused after proper handling, you can also review DES Technologies’ Phoenix Certified process for hardware that is tested and prepared for trusted redeployment.
5. Request Certificates and Final Reports
A disposal vendor should provide more than a pickup receipt. For healthcare assets, request documentation that supports your internal records and audit needs.
Useful documentation includes:
- Certificate of data destruction
- Serialized asset report
- Chain of custody record
- Recycling certificate, when applicable
- Buyback or settlement report
- Missing asset or exception report
Keep these records with your compliance files. They help prove that your organization followed a controlled disposal process.
6. Confirm Vendor Responsibilities
If a vendor handles PHI or ePHI on your behalf, your organization may need a business associate agreement. You should also confirm how the vendor handles data destruction, downstream recycling, employee access, transport, and reporting.
Before equipment leaves your facility, ask:
- Will data destruction happen before resale?
- Can the vendor provide asset-level documentation?
- Can they support NIST 800-88 sanitization?
- What happens to failed or damaged drives?
- Will they identify assets with resale value?
- Can they support bulk pickup from multiple locations?
The right partner should make the process easier for IT, compliance, and finance.
HIPAA Disposal Table: What to Do by Asset Type
| Asset Type | Disposal Risk | Recommended Action |
|---|---|---|
| Laptops and desktops | Local files, cached credentials, patient documents | Inventory, sanitize drives, document serial numbers, resell or recycle after data destruction |
| Servers | EHR data, databases, backups, virtual machines | Decommission carefully, sanitize or destroy drives, maintain chain of custody |
| Hard drives and SSDs | Direct data storage | Sanitize if reusable; physically destroy if failed, encrypted status is unknown, or policy requires destruction |
| Backup tapes | Long-term PHI archives | Track by serial number, purge or destroy based on policy, document final disposition |
| Printers and copiers | Stored scans, print jobs, address books | Check internal storage, wipe or remove drives, document disposal |
| Network equipment | Configurations, logs, access credentials | Reset, remove configs, inventory serial numbers, evaluate resale value |
Common Disposal Mistakes to Avoid
Many HIPAA disposal problems start with small shortcuts. These shortcuts can create big risks later.
Avoid these mistakes:
- Throwing drives or devices into unsecured storage
- Relying only on a basic factory reset
- Selling equipment before data destruction is complete
- Accepting a receipt instead of asset-level reporting
- Forgetting printers, copiers, and backup media
- Failing to track missing or unverified assets
- Using a vendor that cannot document the process
If your team cannot prove what happened to the asset, it may be hard to defend the disposal process later.
How We Buy Used IT Equipment Can Help
We Buy Used IT Equipment helps healthcare organizations, MSPs, enterprises, schools, and government teams retire used IT equipment securely. We buy equipment with remaining market value, support secure logistics, and help document the process.
Our process can help with:
- Bulk healthcare IT refreshes
- EHR server retirements
- Laptop and desktop upgrades
- Storage and drive lots
- Data center decommissioning
- Asset recovery and resale
- Secure recycling for non-resalable equipment
You can start by submitting an equipment list with make, model, quantity, condition, and any known storage details. From there, our team can review resale value, logistics, data destruction needs, and documentation requirements.
Ready to Retire Healthcare IT Equipment Safely?
If your organization is planning a hardware refresh, office cleanout, data center project, or bulk equipment sale, We Buy Used IT Equipment can help you protect data and recover value.
Submit your equipment list today to get a fast quote and discuss secure disposal documentation for your project.
FAQ
What is a HIPAA disposal checklist?
A HIPAA disposal checklist is a step-by-step guide for retiring records, devices, and electronic media that may contain PHI or ePHI. It helps teams inventory assets, protect data, document chain of custody, and confirm final disposition.
Does HIPAA require hard drives to be destroyed?
HIPAA does not require one disposal method for every hard drive. Depending on the risk and policy, drives may be cleared, purged, or physically destroyed. Many organizations choose physical destruction for failed, high-risk, or unknown drives.
Can healthcare organizations sell used IT equipment?
Yes. Healthcare organizations can sell used IT equipment if PHI and ePHI are properly removed or destroyed first. The process should include inventory, secure handling, data destruction, and documentation.
What documentation should I keep after IT equipment disposal?
Keep chain of custody records, serialized asset reports, certificates of data destruction, recycling certificates, settlement reports, and any exception or missing asset reports.
Is deleting files enough before disposal?
No. Deleting files or emptying the recycle bin is not enough. Data can often be recovered unless the media is properly sanitized or destroyed using an appropriate method.