Here’s a number worth knowing before you shop for security tools. In Verizon’s 2026 Data Breach Investigations Report, exploiting software vulnerabilities was the most common way attackers got in, at 31% of breaches. It passed stolen credentials for the first time in the report’s 19-year history. And edge devices and VPNs, the firewalls and gateways that guard your network, made up 22% of those exploitation breaches, up from 3% a year earlier.
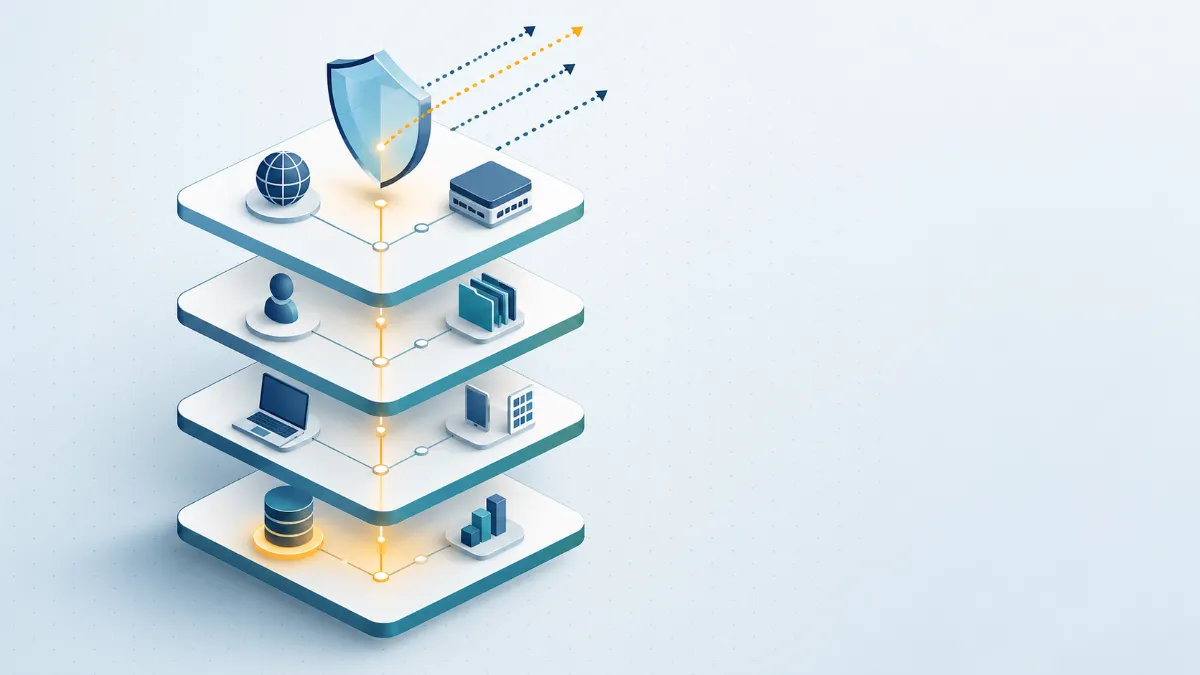
Ransomware showed up in 48% of breaches too. So “network security protection” isn’t one product. It’s a stack of layers, and each layer covers a different gap.
This guide covers 12 essential types, grouped by what they protect. Then it covers a layer that most security lists skip: what happens to your gear when you retire it.
Why Layers Matter
No single tool stops everything. Security teams use “defense in depth,” which means stacking controls so that when one fails, another catches the problem. The NIST Cybersecurity Framework 2.0 organizes this around six functions: Govern, Identify, Protect, Detect, Respond, and Recover. The 12 types below map onto those functions.
Layer 1: Protecting the Network Itself
1. Firewalls
A firewall filters traffic based on rules, deciding what can enter or leave a network. Next-generation firewalls add deeper inspection, application awareness, and built-in intrusion prevention.
- Best for: Every network, at the edge and between internal zones
- Watch out: Firewalls are edge devices, and attackers target them. Keep yours patched, and replace any that your vendor no longer supports.
2. Intrusion Detection and Prevention (IDS/IPS)
An IDS watches traffic and alerts you to suspicious activity. An IPS goes further and can block it automatically. Many next-generation firewalls include both.
- Best for: Spotting attacks and known malicious patterns in real time
- Watch out: Poorly tuned systems flood teams with false alarms, so plan time for tuning.
3. VPNs and Zero Trust Network Access
A VPN encrypts traffic between a device and your network, which helps remote workers connect safely. Zero trust network access takes a stricter approach. It grants access to specific applications based on identity and device health, instead of opening the whole network. NIST SP 800-207 defines zero trust architecture.
- Best for: Remote and hybrid teams
- Watch out: A traditional VPN can give a connected user broad reach, and VPN appliances are a favorite attack target. Patch them quickly.
4. Network Segmentation
Segmentation divides a network into smaller zones, such as separate areas for guests, servers, cameras, and point-of-sale systems, with rules controlling traffic between them. If an attacker gets into one zone, segmentation limits how far they can move.
The original version of this post described segmentation as grouping users by “level of expertise or interest in a topic.” That’s not right. It’s about separating systems by function and risk.
- Best for: Limiting damage from any breach
- Watch out: Design it carefully. Poorly planned segments break applications.
5. Web and DNS Filtering
Web filters and DNS filtering block known malicious or unwanted sites before devices connect to them. A proxy server can act as the gateway for this traffic and enforce policy.
- Best for: Stopping phishing links and malware downloads
- Watch out: A proxy doesn’t protect personal information by itself. It’s one control among several.
6. Wireless Security
Secure your Wi-Fi with modern encryption (WPA3 where your equipment supports it), strong passphrases, and a separate guest network. Larger organizations often use individual logins instead of a shared password.
- Best for: Any office or site with Wi-Fi
- Watch out: Old access points may not support current standards, which is another reason to refresh aging gear.
Layer 2: Protecting Access and Identity
7. Identity and Access Management, Including MFA
Strong identity controls verify who’s logging in and limit what they can reach. Multi-factor authentication adds a second proof, such as an authenticator app, a hardware key, or a passkey. Phishing-resistant options are the strongest. Text-message codes are better than nothing, but weaker. Apply least privilege, so people can access only what their job needs.
- Best for: Every account, especially email, admin tools, and remote access
- Watch out: MFA fatigue attacks and stale accounts. Review access regularly.
Layer 3: Protecting Devices and Applications
8. Endpoint and Mobile Security
Endpoint security protects laptops, desktops, servers, and phones. Traditional antivirus uses signatures to catch known malware. Modern endpoint detection and response (EDR) tools also watch behavior and can isolate an infected device. Mobile device management helps secure phones and tablets.
The old post listed “antivirus,” “security software,” and “antimalware” as three separate items. They overlap, and antivirus alone is no longer enough, since malware often evades signature-based detection.
- Best for: Every device that touches your network
- Watch out: Unpatched devices. Keep operating systems and apps updated.
9. Email Security
Email is still a top route for phishing and malware. Email security filters malicious messages and attachments. Email authentication standards, including SPF, DKIM, and DMARC, help stop attackers from spoofing your domain.
- Best for: Every organization
- Watch out: No filter catches everything, so pair it with employee training.
10. Web Application Firewalls (WAF)
A web application firewall protects websites and web apps from attacks like SQL injection and cross-site scripting.
- Best for: Any business with a customer-facing site or portal
- Watch out: A WAF doesn’t fix insecure code. It adds a protective layer.
Layer 4: Protecting Data and Responding
11. Data Protection: Encryption, DLP, and Backups
Encryption scrambles data so unauthorized people can’t read it, both in transit and at rest. Data loss prevention (DLP) tools monitor and block sensitive data from leaving your control. And backups, ideally with an offline or immutable copy, are your safety net against ransomware.
- Best for: Every business that stores customer, employee, or financial data
- Watch out: Untested backups. Run restore tests.
12. Monitoring and Response
Security information and event management (SIEM) collects logs from across your environment and flags suspicious patterns. Vulnerability management finds and fixes weaknesses, which matters because exploitation was the top breach entry point in Verizon’s 2026 report. An incident response plan tells your team what to do when something goes wrong.
The cost of a breach makes this worth the effort. IBM’s 2025 report puts the global average at $4.44 million, and $10.22 million in the United States. It also found that organizations using AI and automation extensively saved about $1.9 million per breach on average. Our guide to AI network management covers how those tools work.
- Best for: Anyone who wants to detect problems early
- Watch out: Collecting logs nobody reads. Assign an owner.
The Layer Most Lists Skip: Retiring Old Equipment
Every device above eventually reaches the end of its life, and that’s a security moment too.
Firewalls, routers, switches, and VPN gateways store configurations, passwords, certificates, VPN keys, and logs. If a retired device walks out the door unwiped, that information can follow. A factory reset doesn’t always meet your security requirements.
The original post also listed “data destruction” twice, with a circular definition. Here’s what it actually means: permanently making data unrecoverable, using erasure or physical destruction. Follow current NIST SP 800-88 Revision 2 guidance, using certified data erasure or physical data destruction, and keep chain of custody records.
Old equipment is also a risk while it’s still running. In February 2026, CISA issued Binding Operational Directive 26-02, which orders federal agencies to inventory and remove end-of-support edge devices, including firewalls, routers, switches, and wireless access points. It applies to federal agencies, but CISA encourages other organizations to follow similar steps. Our guide to replacing networking gear explains how often to refresh and what to watch for.
What We Left Out
Some older lists include identity theft protection and parental controls. They’re useful consumer tools, but they aren’t network security controls, so we left them out.
The 12 Types at a Glance
| Type | What It Does | Layer |
|---|---|---|
| Firewalls | Filter traffic by rules | Network |
| IDS/IPS | Detect and block threats | Network |
| VPN and zero trust access | Secure remote access | Network |
| Network segmentation | Limit movement between zones | Network |
| Web and DNS filtering | Block malicious sites | Network |
| Wireless security | Protect Wi-Fi | Network |
| Identity and access management | Verify users, limit access | Identity |
| Endpoint and mobile security | Protect devices | Devices |
| Email security | Stop phishing and spoofing | Applications |
| Web application firewall | Protect websites and apps | Applications |
| Data protection | Encrypt, prevent leaks, back up | Data |
| Monitoring and response | Detect and respond to incidents | Response |
Selling Your Old Security and Networking Gear
When it’s time to upgrade, our partner site WeBuy Used IT Equipment buys used networking equipment, including firewalls, switches, and routers. Here’s how it works:
- Send us your list with the equipment type, quantity, and condition.
- Get a quote. We review your list and send an offer.
- We cover shipping. See our secure shipping details.
- We erase the data. Every device is processed through our Phoenix Certified process.
- You get paid, with documentation. A Certificate of Data Destruction comes with your payment.
Our network equipment buyback guide and equipment buyback guide walk through the process. For smaller teams, see our ITAD best practices for small and medium-sized businesses. Large projects can include full data center lots, and anything without resale value goes through R2v3-certified electronics recycling.
Frequently Asked Questions
What are the main types of network security?
The core types include firewalls, intrusion detection and prevention, VPNs and zero trust access, network segmentation, web and DNS filtering, and wireless security. Layered on top are identity controls, endpoint and email security, web application firewalls, data protection, and monitoring and response.
What’s the difference between IDS and IPS?
An intrusion detection system watches traffic and alerts you to suspicious activity. An intrusion prevention system can also block it automatically. Many next-generation firewalls include both.
Is antivirus enough to protect a network?
No. Antivirus catches known malware, but modern attacks often evade it. Use layered defenses, including endpoint detection and response, patching, email security, MFA, and backups.
What is network segmentation?
It divides a network into separate zones, such as guests, servers, and point-of-sale systems, with rules controlling traffic between them. If attackers get into one zone, segmentation limits how far they can spread.
What is zero trust?
Zero trust assumes no user or device is trusted by default. It grants access to specific resources based on identity and device health, and it keeps verifying. NIST SP 800-207 describes the architecture.
What should I do with old firewalls and switches?
Remove them from your monitoring and access systems, revoke their credentials, and sanitize them following NIST SP 800-88 Revision 2. Then check whether they have resale value before you recycle them.
The Bottom Line
Network security isn’t one tool. It’s a set of layers, from firewalls and segmentation to identity, endpoints, data, and response. And it extends to the end of every device’s life.
Retiring old network gear? Get a quote to recover value, and read our FAQ for answers about the process. You can also explore our partner’s ITAD services.